Cyberattack Headlines Are Everywhere—What Are We Doing to Protect Your Website?
Cyberattack headlines can make any business owner uneasy. Your website may be where customers find you, request a quotation, make a booking, submit information, or decide whether your company looks trustworthy.
It is reasonable to ask what is being done to protect it.
The honest answer is not that any website can be made completely invulnerable. Official WordPress guidance describes security as risk reduction, not risk elimination. Good website care combines several practical safeguards so problems are less likely, suspicious activity is noticed sooner, and recovery is possible when something does go wrong.
For websites covered by a NetizenWorks hosting or maintenance arrangement, our work follows the scope of each account. That may include software updates, backup review, availability and security alerts, checks of important website functions, and a practical response when an issue requires action.
Security is a process, not a one-time product
A business website is not one piece of software. It may depend on WordPress, a theme, plugins, forms, email delivery, analytics, payment or booking services, hosting, domain settings, and the devices used to administer it.
Each part can change. Software receives security fixes. A third-party service can alter its requirements. A password can be exposed through an unrelated breach. A convincing email can trick someone into giving away access even when the website itself is working normally.
That is why responsible security cannot be reduced to installing one plugin or placing a padlock icon on a page. It requires layered protection, regular attention, and clear responsibilities.
What website maintenance contributes to security
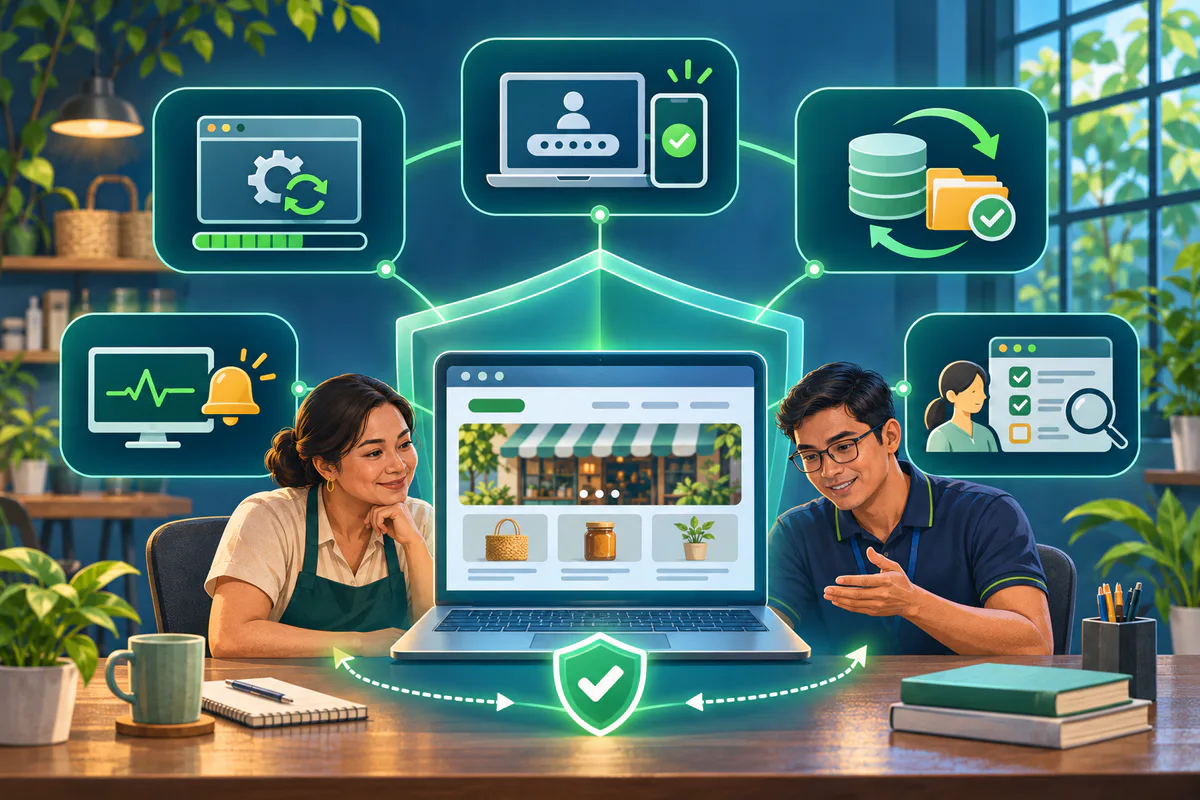
Maintenance helps reduce avoidable weaknesses before they become emergencies. Depending on the website and its service arrangement, this can include:
- reviewing WordPress, theme, and plugin updates;
- applying appropriate fixes in a controlled way;
- checking that important pages and forms still work after changes;
- reviewing backup and availability information;
- paying attention to credible security alerts;
- removing unnecessary components when it is safe to do so; and
- documenting issues that need follow-up.
Updates matter because old software can contain publicly known weaknesses. However, installing every update without preparation can also create compatibility problems. A sensible process considers urgency, dependencies, recovery options, and the functions that should be tested afterward.
Backups are part of security—but only if they are useful
A backup does not prevent an attack. Its purpose is to help restore files, content, configuration, or business data after damage, deletion, failure, or compromise.
That makes backup quality more important than the comforting appearance of a “backup enabled” label. A useful recovery plan considers what is being backed up, how recent the copy is, where it is stored, who can access it, and whether the important parts of the website can actually be restored.
The appropriate backup frequency depends on the website. A small informational site and a busy online store do not change at the same rate or carry the same potential data loss. Website owners should understand what their own arrangement includes rather than assuming every website follows one universal schedule.
Monitoring helps us respond; it does not remove all risk
Availability and security alerts can draw attention to downtime, unusual behavior, failed jobs, storage pressure, or other conditions that deserve review. They are valuable because many website problems first appear behind the scenes.
Monitoring is not the same as a promise that a person is watching every website every second. Automated systems can produce false alarms or miss context. The responsible approach is to investigate credible alerts, compare them with the website’s actual condition, and communicate when a specific account needs action.
If we identify an issue that affects your website, our goal is to tell you what we know, what it means for your account, what has already been done, and what decision or cooperation may be needed from you.
Your own accounts and decisions are part of the security boundary
Website security does not stop at the hosting server. Administrator email accounts, domain accounts, payment services, staff devices, password managers, and shared credentials can all affect the website.
The US Cybersecurity and Infrastructure Security Agency’s Secure Our World guidance emphasizes four practical habits: recognize and report phishing, use strong passwords, turn on multifactor authentication, and update software.
- Use a long, unique password for every important account.
- Enable multifactor authentication wherever it is available.
- Limit administrator access to people who genuinely need it.
- Remove access promptly when staff or providers change.
- Keep administration computers and browsers updated.
- Report suspicious messages or unexpected website behavior quickly.
Security works best when the website provider and business owner both protect their part of the system.
Verify unusual messages before paying or sharing access
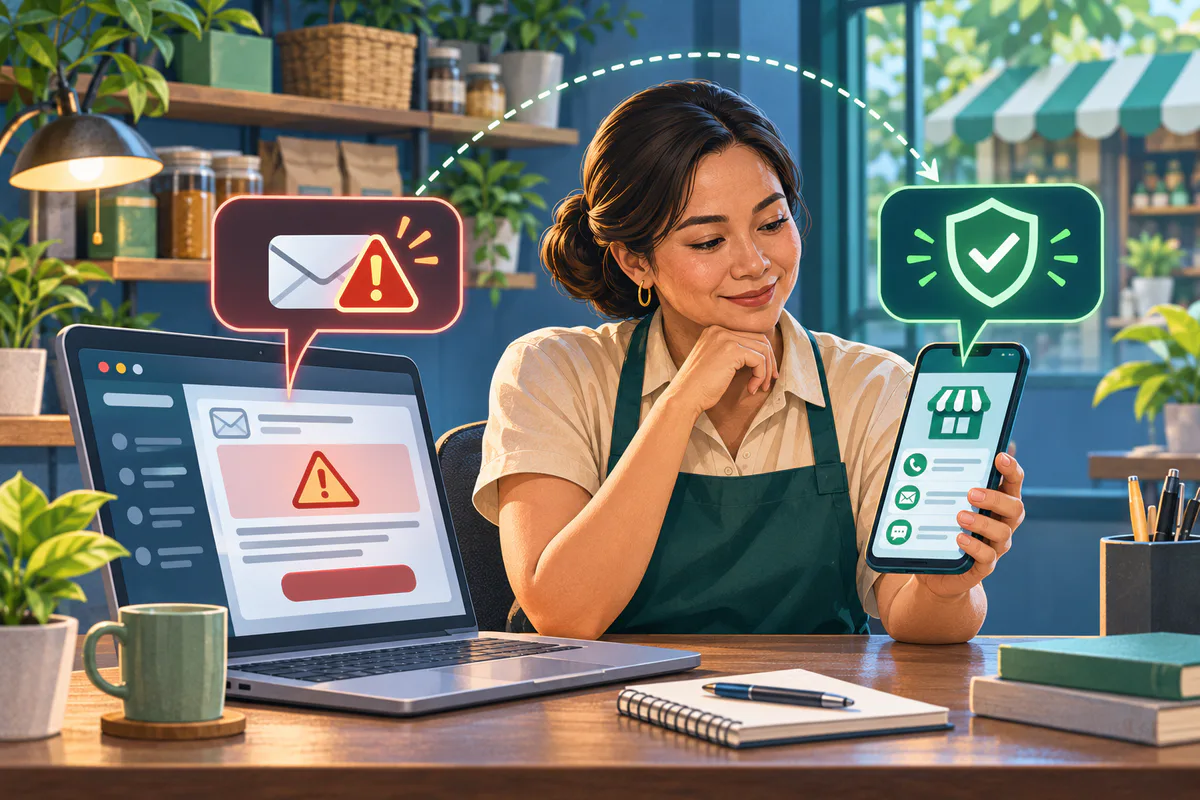
Cybercriminals do not always attack the website directly. Sometimes they imitate a provider, copy a familiar signature, invent an urgent renewal, or claim that immediate payment is required to prevent suspension.
Urgency is not proof. Branding is not proof. A familiar-looking name is not proof.
If a message asks for a password, verification code, payment, account transfer, or unexpected remote access, pause and verify it through a contact method you already trust. Do not use the suspicious message’s own link or telephone number as your only confirmation.
NetizenWorks will never need your password or multifactor authentication code through an unexpected email. Open our official website independently and use the NetizenWorks contact page to confirm anything unusual. Our scam-awareness guide provides additional steps.
What we can promise—and what no responsible provider should promise
We should not promise that your website will never receive an attack, experience downtime, or encounter a technical problem. The internet is a changing environment, and some risks sit outside any one provider’s control.
What we can commit to is a disciplined approach within the scope of your account:
- practical maintenance rather than panic;
- attention to credible alerts;
- reasonable care with updates and recovery points;
- clear communication when a verified issue affects you; and
- honest advice about responsibilities, limitations, and next steps.
There is no general emergency action required from NetizenWorks clients simply because cyberattack news is prominent. If your website needs a specific change, we will contact you with information that applies to your account.
Frequently asked questions
Does a maintained website become impossible to hack?
No. Maintenance reduces avoidable risk and improves readiness, but it cannot remove every possible vulnerability, credential theft, service failure, or human mistake.
Should every update be installed immediately?
Urgent security fixes may need prompt attention. Other updates should still be reviewed in light of compatibility, recovery options, and the website functions that must be tested after the change.
What should I do if I receive a suspicious NetizenWorks message?
Do not send credentials, verification codes, or payment based on the message alone. Contact us through a method you already trust or through our official website.
What should I do if I notice unusual website behavior?
Record the page, approximate time, device, and any message shown. Contact us promptly and avoid unrelated changes that could erase useful evidence.
Conclusion: calm preparation is stronger than fear
Cybersecurity headlines deserve attention, but fear is not a maintenance strategy. A stronger response is to keep software current, maintain usable recovery options, watch for credible signs of trouble, protect access, verify unusual requests, and know who is responsible for each part of the system.
That is the approach NetizenWorks continues to follow for covered websites: steady care, practical safeguards, honest limitations, and clear action when a real issue requires it.
If you are unsure what your current website arrangement includes, contact NetizenWorks. We can review the relevant account before making any plan-specific statement or recommendation.
The editorial illustrations are AI-generated. They do not depict a real client, incident, monitoring screen, or security event.